
Security: Key Rotation of our Azure Storage account keys

Azure Storage account key rotation is one of the most important things people forget about. Account keys provide full access to your storage; nevertheless, we fail to keep them safe and fresh. 

In this article, we talk about the key rotation mechanisms provided by Microsoft Azure. 

Why?

Azure Storage account provides two account keys that can manage the storage. They provide the user with the full power to read, modify, delete and create content. Not only that we need to keep them safe, but we also need to ensure that we rotate them at specific time intervals. 

Key expiration policy

A key expiration policy can be easily created from the Azure Portal. When the policy is triggered, a reminder is displayed in the portal to remind us to rotate the keys. Additionally, once you have the key expiration policy defined, you can monitor the compliance of your storage account, including the key rotation.


As you can see above, this can be achieved from the Azure Portal or through the Azure CLI or PowerShell. The reminders can be daily, weekly, monthly or yearly OR custom.

Monitoring expired account keys

This can be achieved using Azure Policies. A built-in policy for Azure Storage covers the account key expiration. The policy can be applied to one storage account or to all storage accounts under a resource group or subscription. 

Once you have defined the policy, you navigate to the Azure Policy dashboard to check the level of compliance. 


Alerts and Notifications

We talked about defining a policy and monitoring the key expiration from the portal or from the Azure Policy dashboard. 

What about automation? Can we configure the policy in such a way as to send a notification to an interval or external system?

YES, we can do this. You would need to rely on Event Grid and ingest the events from Azure Policy. Once you have done this, you can decide what kind of action (event handled you would like) - Azure Functions, Logic App or Service Bus, Queues, WebHooks, Automation and so on.

You could even define an Azure Automation or an Azure Function that automatically rotate the key when the Azure Policy is triggered. 
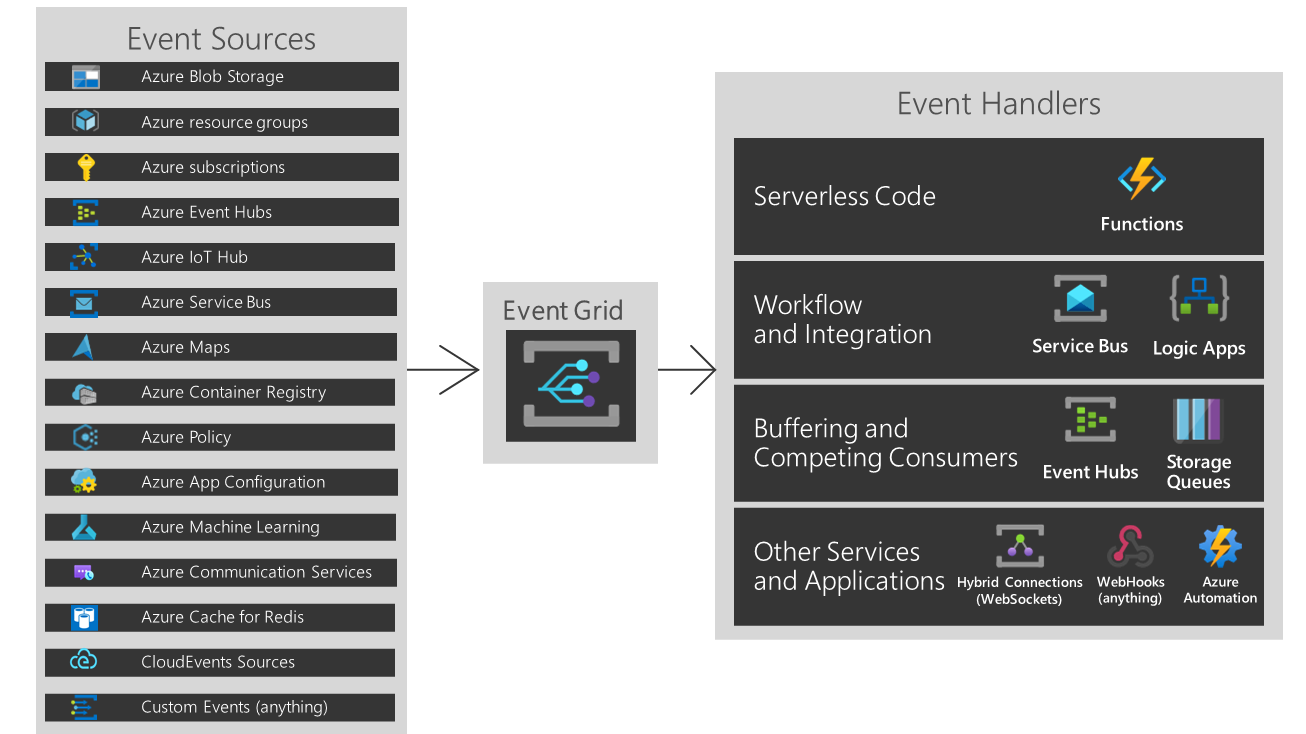

For more about how to react when an Azure Policy state changes, I recommend looking at this page.

Conclusion

Microsoft is offering us the capability to define alerts and policies, monitor them, and react to them. Azure Key Rotation capability is fully covered by Azure; we just need to ensure that we are configuring and integrating it in our systems. 

Comments

Popular posts from this blog

How to audit an Azure Cosmos DB

In this post, we will talk about how we can audit an Azure Cosmos DB database. Before jumping into the problem let us define the business requirement: As an Administrator I want to be able to audit all changes that were done to specific collection inside my Azure Cosmos DB. The requirement is simple, but can be a little tricky to implement fully. First of all when you are using Azure Cosmos DB or any other storage solution there are 99% odds that you’ll have more than one system that writes data to it. This means that you have or not have control on the systems that are doing any create/update/delete operations. Solution 1: Diagnostic Logs Cosmos DB allows us activate diagnostics logs and stream the output a storage account for achieving to other systems like Event Hub or Log Analytics. This would allow us to have information related to who, when, what, response code and how the access operation to our Cosmos DB was done. Beside this there is a field that specifies what was th...

Can User Technical Profile Influence AI Architecture Decisions?

In the last few days, I ran a small experiment on Devin/Windsurf/Cascade, BMAD, and LLM-based architecture decisions. The initial concern was simple: if an AI coding assistant knows something about the user, for example, that the user is a Java developer or a .NET developer, can this information influence the architecture and technology stack that the AI will propose? This question is important because many companies are starting to use AI tools not only for coding but also for product discovery, architecture, documentation, and technical decision-making. If the AI is influenced by the developer's personal profile, the result may not be fully neutral. It may look like a business or architecture decision, but in reality, it may be partially shaped by the context of the person using the tool. The test was done using BMAD with Devin/Windsurf/Cascade. The scenario was a unified field service operations platform. The task was to let BMAD refine the product, define the architecture and s...

ADO.NET provider with invariant name 'System.Data.SqlClient' could not be loaded

Today blog post will be started with the following error when running DB tests on the CI machine: threw exception: System.InvalidOperationException: The Entity Framework provider type 'System.Data.Entity.SqlServer.SqlProviderServices, EntityFramework.SqlServer' registered in the application config file for the ADO.NET provider with invariant name 'System.Data.SqlClient' could not be loaded. Make sure that the assembly-qualified name is used and that the assembly is available to the running application. See http://go.microsoft.com/fwlink/?LinkId=260882 for more information. at System.Data.Entity.Infrastructure.DependencyResolution.ProviderServicesFactory.GetInstance(String providerTypeName, String providerInvariantName) This error happened only on the Continuous Integration machine. On the devs machines, everything has fine. The classic problem – on my machine it’s working. The CI has the following configuration: TeamCity .NET 4.51 EF 6.0.2 VS2013 It see...